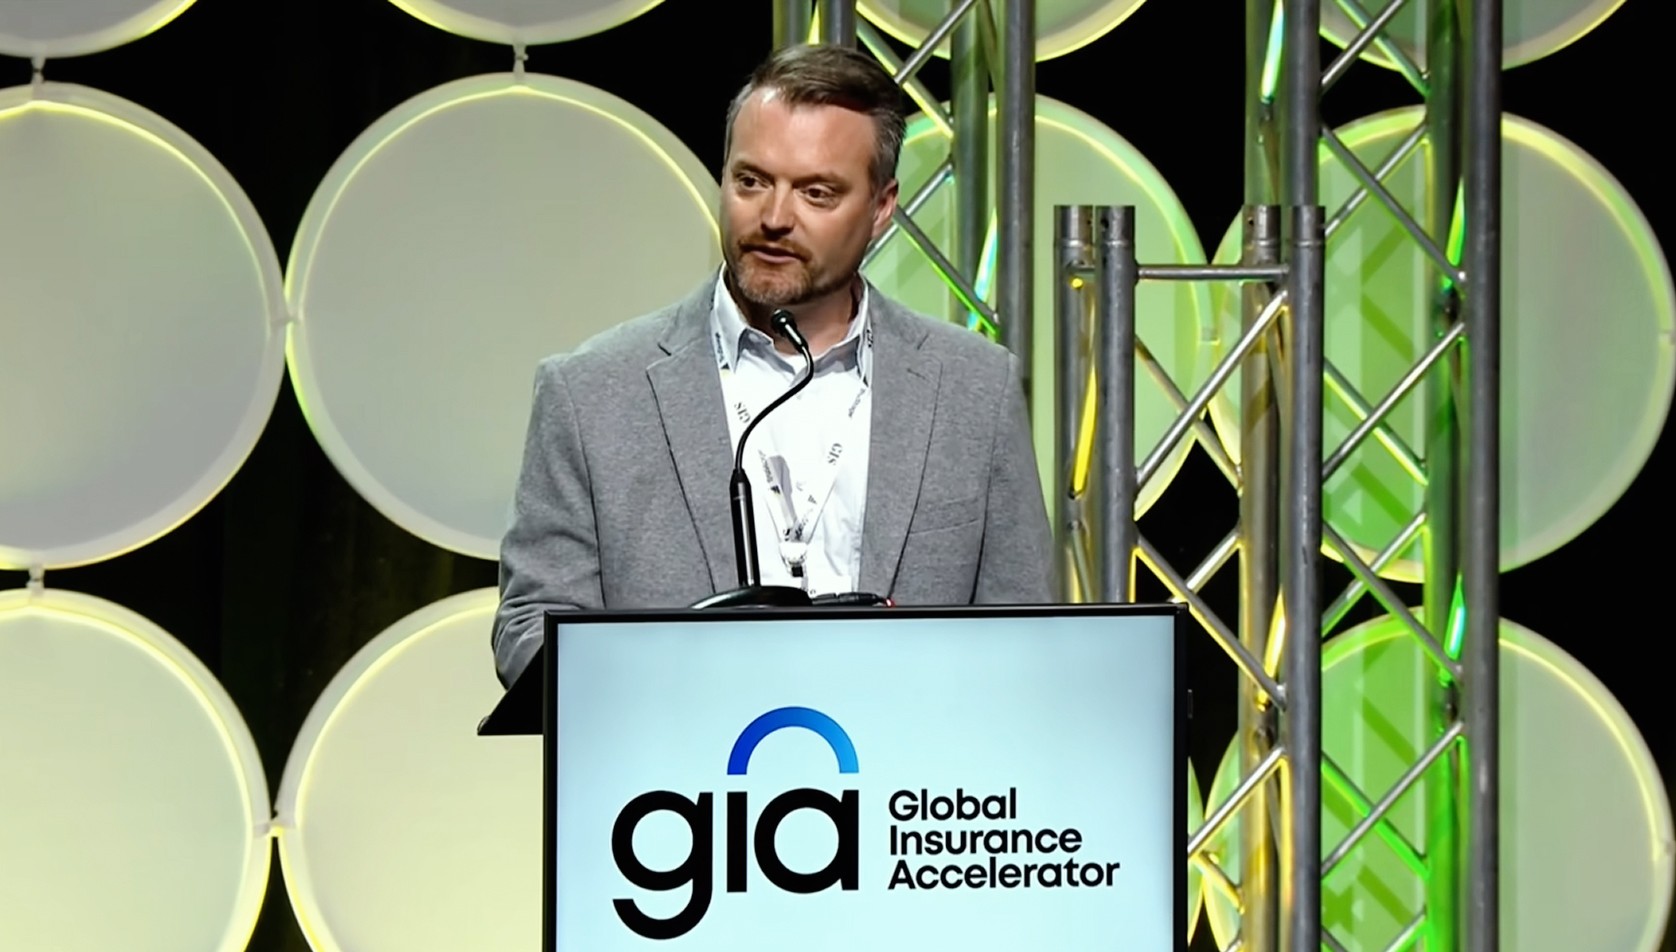


Mike Brady uses NASCAR to explain how insurance technology has changed and why cyber consequences now matter financially.
Read the Risk Tales postIllustrative example · not a coverage determination
Find out what could cause the loss, what you can prevent and what insurance may cover.
Modelled cyber loss
$4.2M
Potential insurance response
$3.0M
Remaining exposure
$1.2M
Explore Astragar
From cyber risk and AI agents to insurance, industry insights and the people behind our mission. Discover what we’re building and who we’re building it with.
01
02
03
04
05
06
01
/
06
Choose your outcome
01
Identify and prioritise the cyber exposures that matter most.
Prioritise My Risks →
02
Understand the potential financial impact of vulnerabilities and sensitive data exposure.
Quantify My Exposure →
03
Assess cyber insurance coverage and identify potential gaps.
Review My Coverage →
04
Connect controls and technical evidence to underwriting, compliance and claims.
Explore the Evidence Layer →
Identify vulnerabilities, sensitive data and threat scenarios associated with your most important assets.
Translate technical cyber risk into potential financial impact.
Compare modelled loss scenarios with relevant limits, sublimits, exclusions and conditions.
Convert important policy conditions into controls that can be assigned, tested, evidenced and attested.
Maintain an evidence trail for security, compliance, underwriting, renewal and claims.
Risk → $ Exposure → Cover → Controls → Evidence
Insurance coverage analysis
Connect a plausible cyber event to financial loss, your controls and your actual policy, so you can see where cover could fall short before it matters, scenario by scenario.
Ransomware
Sensitive-data breach
Business interruption
Third-party incident
Critical vulnerability exploitation
AI-agent incident
Illustrative example
Scenario
Ransomware
↓
Modelled loss
$4.2M
↓
Insurance response
$3.0M
↓
Potential exposure gap
$1.2M
For the insured
Connect everyday security work directly to insurance outcomes.
01
02
03
04
05
06
07
08
Make the policy operational
Astragar extracts important conditions and requirements from your cyber insurance policy and converts them into controls.
The insured can assign them, test them, attach evidence and attest to them.
The result is a continuously developing evidence record that supports the insured's security programme and gives insurers better information for underwriting, monitoring, renewal and claims.
Cyber insurance policy
↓
Limits · Sublimits · Exclusions · Conditions · Requirements
↓
Astragar
↓
Controls
↓
Test → Evidence → Attest
↓
Underwrite → Monitor → Renew → Claim
For the insurer
01
Understand actual vulnerabilities, sensitive data, controls and financial exposure. Use better evidence to support risk selection and policy design.
02
Convert important policy conditions into controls the insured can test, evidence and attest during the policy period. Spot changing risks and control gaps before renewal or a claim.
03
See how the insured's risk, exposure and control posture changed during the policy period. Use accumulated evidence to support renewal decisions.
04
Assess the claim against an established evidence trail, rather than reconstructing the insured's security posture after the incident.
Underwrite → Monitor → Renew → Claim
150
conversations with carriers, brokers and enterprises coming out of the Global Insurance Accelerator.
Aeguard · AI-agent & endpoint evidence
Astragar combines evidence from your vulnerabilities, sensitive data, controls and endpoints.
Aeguard extends that evidence layer to AI-agent behaviour, creating tamper-evident records of what agents were permitted to do and what they actually did.
Your evidence, not our score
Astragar doesn't ask you to trust another opaque cyber score.
Risk is calculated from your assets, vulnerabilities, sensitive data, controls and evidence, and measured against your own changing risk profile.
As threats, vulnerabilities, assets and policies change, your exposure is re-measured against your own evidence-based benchmark, rather than relying on generic vendor baselines.
Insurance meets GRC
Insurance conditions, security controls and compliance frameworks shouldn't be run as separate programmes.
Astragar connects them through common controls and evidence, so the same control, tested once, supports your policy requirements and your frameworks.
Policy requirement
+
NIST · ISO 27001 · SOC 2 · NYDFS · DORA
↓
Common control
↓
Test → Evidence → Attest
For Insureds
Find your most material vulnerabilities and sensitive data. Quantify the exposure. Compare it with your cover. Turn policy conditions into controls and maintain the evidence you may need if a claim occurs.
Explore Astragar for Insureds →
For Insurers
Connect cover to the insured's actual risk. Convert policy conditions into controls the insured can test, evidence and attest. Use that evidence to support underwriting, ongoing risk management, renewals and claims.
Explore Astragar for Insurers →
For Insurers · Treaty
We're developing portfolio-level views with early partners: evidence on exposure and control posture across your cyber book, to support treaty placement and renewal with more than loss history alone.
Explore Treaty & Reinsurance →
Low-friction first step
Security analysts
Identify financially significant vulnerabilities.
See the Offer →
CISOs
Prioritise major risks.
Start an Assessment →
CFOs and risk managers
Explore financial exposure and policy gaps.
Review My Coverage →
Insurers
Test evidence against a specific underwriting decision.
Discuss a Pilot →
AI security teams
Assess AI-agent access, permissions and behaviour.
Explore Aeguard →
Get Covered