
In the year to 16 January 2026, SDAIA's violation committees issued 48 decisions under the Personal Data Protection Law. For security leaders the most important line in that record is one of the four behaviours penalised: inadequate technical and organisational safeguards.
What was penalised
Behaviour penalised | Needs a breach? | Who usually owns the evidence |
|---|---|---|
Processing without a legal basis | No | Privacy and legal |
Disclosure without justification | No | Privacy, data owners |
Inadequate technical and organisational safeguards | No | Security |
Marketing without consent | No | Marketing and privacy |
None of the four needs an incident to trigger. The decisions came from the paperwork and the controls, not from attackers.
Why that changes the security brief
Most security programmes in the Kingdom are built around preventing and responding to incidents. That is still the right goal. But the enforcement record shows a second test running alongside it: can you show that the safeguards were adequate before anything happened?
That is an evidence question, not a tooling question. A control that works but cannot be evidenced looks the same to an auditor as a control that does not exist.
An untested control and a missing control look identical in an audit file.
In plain language
"Adequate safeguards" will be judged on what you can show: which controls exist, which data they protect, how you know they work, and when you last checked.
Making safeguards defensible
Tie controls to data. Start from where personal data and sensitive data actually sit, then show which controls protect those systems.
Evidence continuously. Configuration exports, access reviews and test results, dated and retained, not assembled the week before an audit.
Prioritise by consequence. Not every gap is equal. Rank them by the data and processes they expose, not by severity score alone.
Put a number on the remainder. Expressing the residual exposure in dollars is what lets a board approve the fix list and what an underwriter recognises.
The penalties are real
PDPL penalties reach up to SAR 5 million per violation and can be doubled on repeat. Disclosure of sensitive data with intent to harm carries up to two years' imprisonment and a SAR 3 million fine. With 48 decisions already issued, the question is no longer whether SDAIA enforces. It is whether your evidence is ready when it does.
Next step. Our PDPL briefing pack covers the four penalised behaviours, registration, transfers and the 72-hour breach clock. Download the briefing pack →
For any comments or information please reach out to info@astragar.com
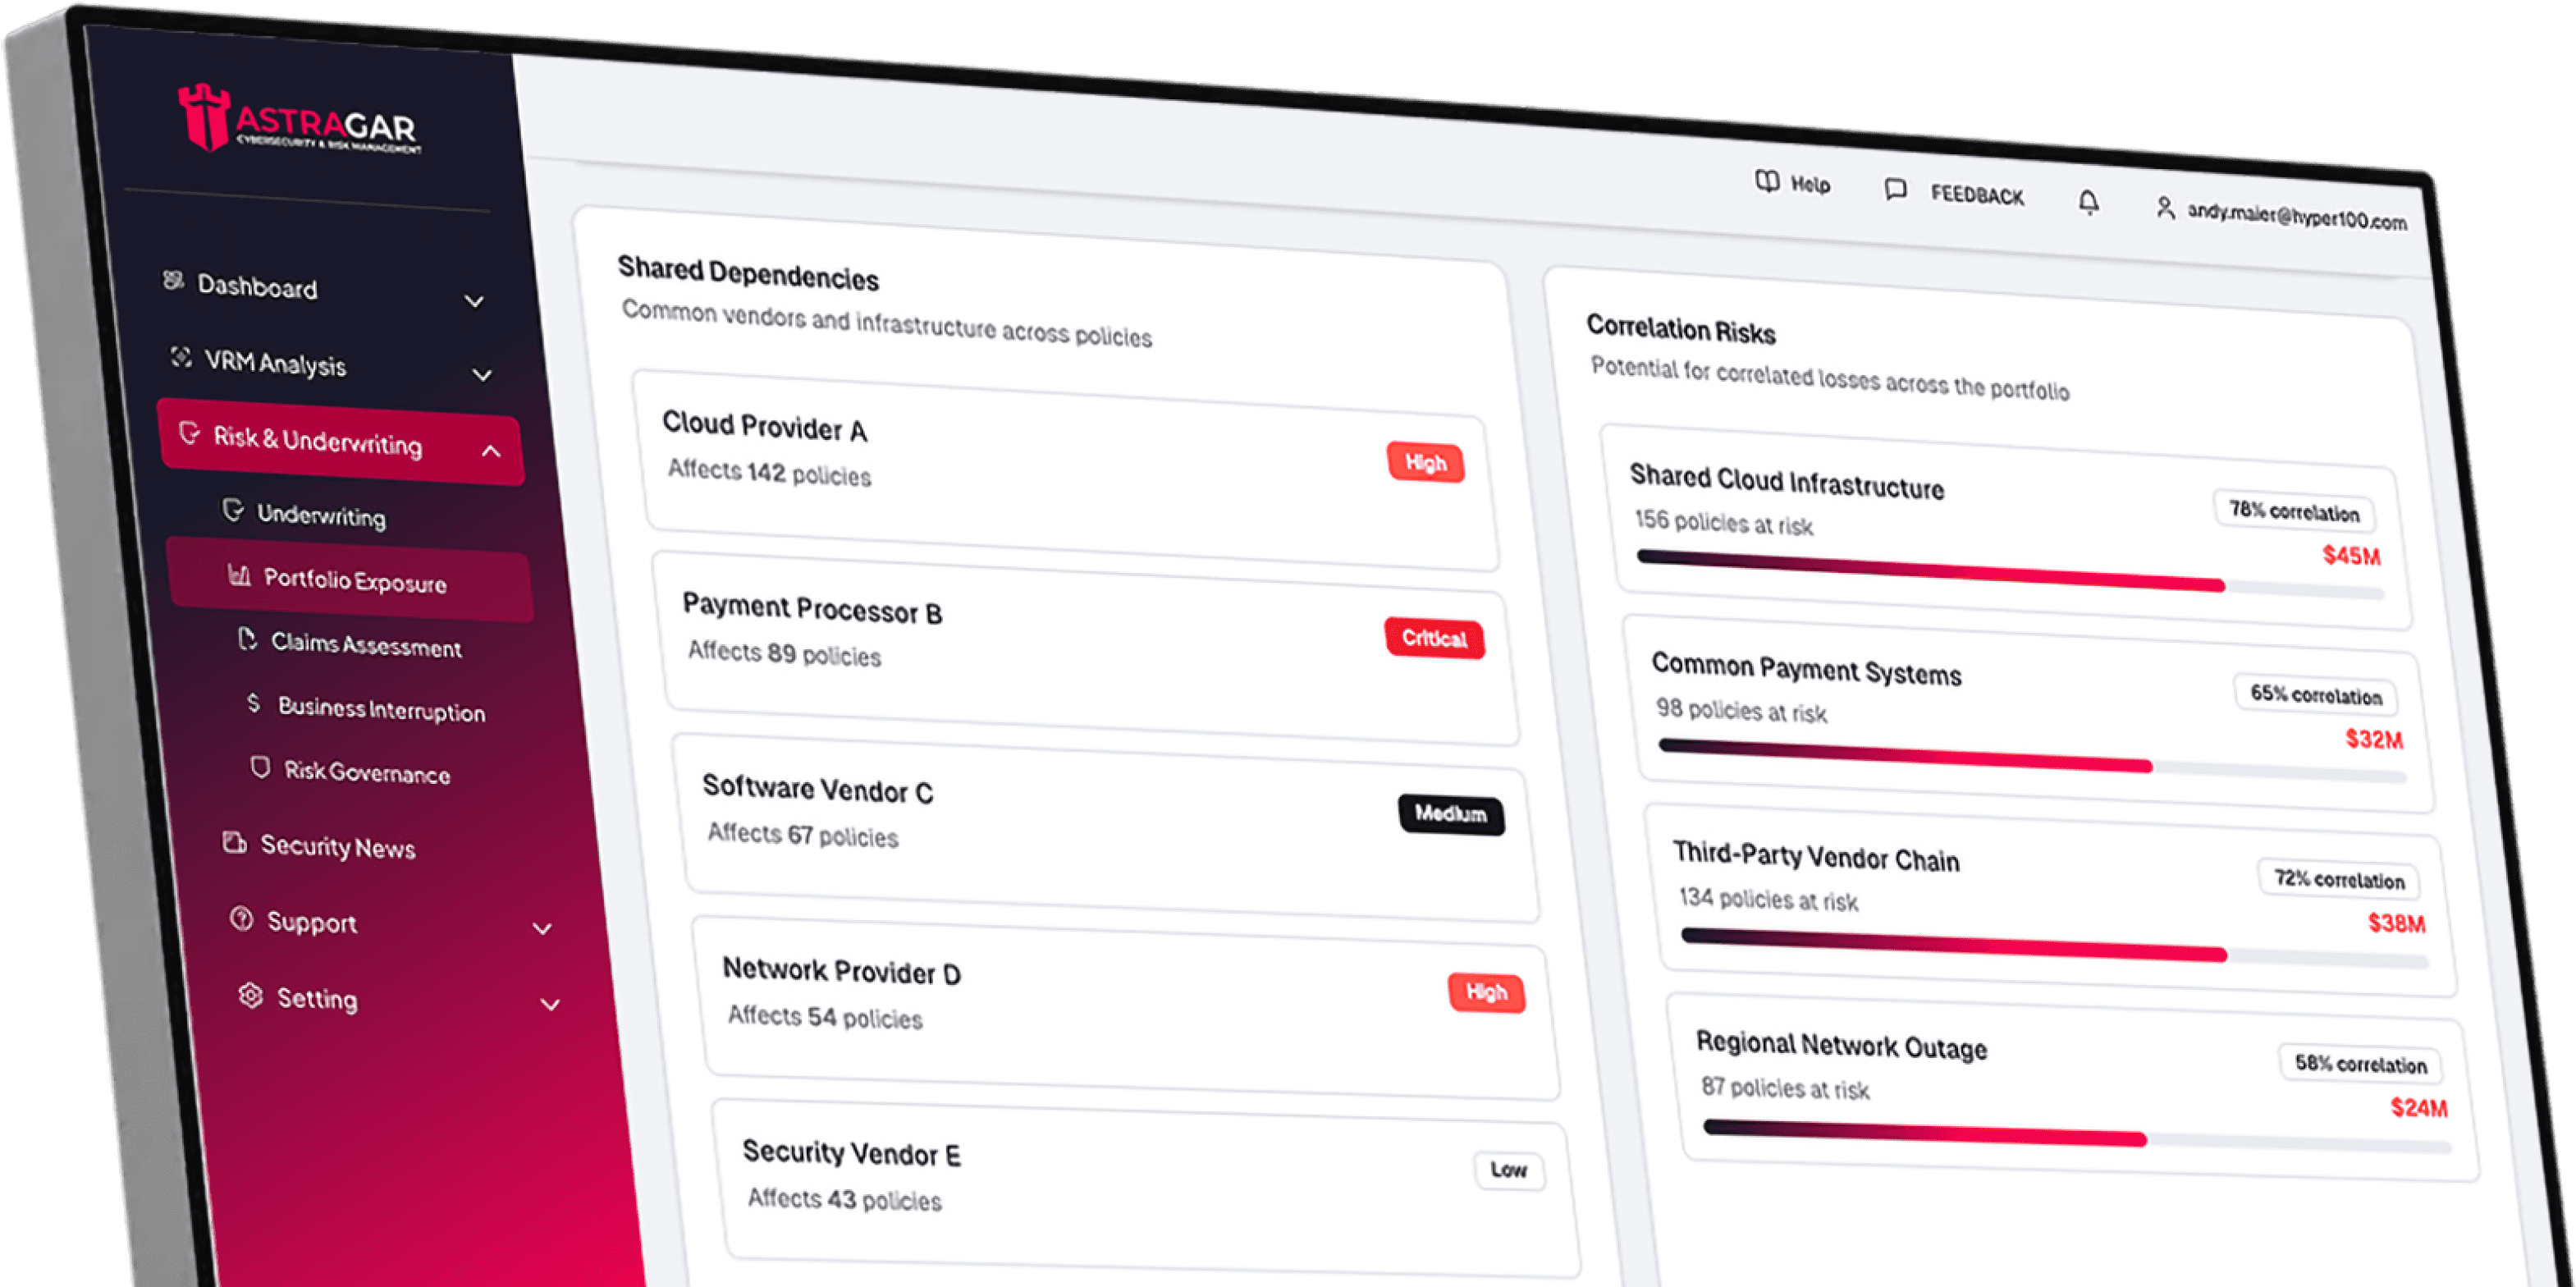

See your cyber risk in $ terms, not CVSS scores.